
Who We Are: TrustLayerLabs
We are offensive security engineers, penetration testers, and compliance advisors providing deep manual security testing and audit readiness for high-growth tech platforms globally.
Eliminating Logic Vulnerabilities That Automated Scanners Miss
Startups move fast and traditional automated scanners throw hundreds of false alerts while missing complex logical vulnerabilities like authorization bypasses (BOLA/IDOR), broken business flows, and tenant boundary leaks.
Our mission is to bridge this gap. We combine human logic, active adversary emulation, and regulatory controls mapping to deliver actionable findings with copy-paste code patches in record time.
Manual Logic Verification
We manually trace API queries, evaluate session scopes, check authorization cookies, and simulate realistic multi-tenant attack paths that tools overlook.
Remediation-First Advisory
We don't just export raw vulnerability lists. We provide concrete code fixes, framework-specific guidance, and complimentary retesting letters for your enterprise buyers.
Practitioner Leadership & Credentials
Direct engagement with certified offensive security specialists
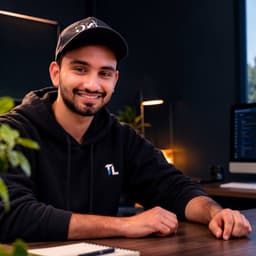
Nagasrinivasa Rao
Founder & Lead Security Architect
Offensive security architect specializing in manual API penetration testing. Holds CEH and CWL C3SA credentials; focuses on authorization logic, BOLA flaws, and web application assessments.
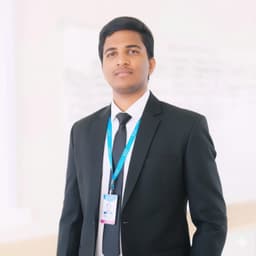
Ramineni Teja
Co-Founder & GRC Lead
Compliance and risk management lead for high-growth startups. Certified ISO/IEC 27001 Lead Auditor, CWL C3SA, and CWL BTF holder; guides teams through ISO 27001 gap analysis, SOC 2 readiness, and security governance.
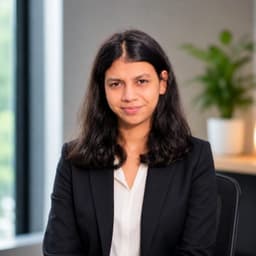
Nayansi Anand
Security Engineer & VAPT Consultant
Application security engineer certified in CEH, specializing in manual web testing, OWASP Top 10 vulnerabilities, and practical developer fix guidance.
Technical Research & Publications
API & Application Research
We document common API authorization gaps, broken object-level access patterns, and developer remediation best practices.
AI & Infrastructure Security
Technical guides on defending Generative AI applications, RAG pipelines, and containerized cloud architectures.
Developer Security Playbooks
Actionable security checklists and engineering playbooks to help startup development teams build secure-by-default software.
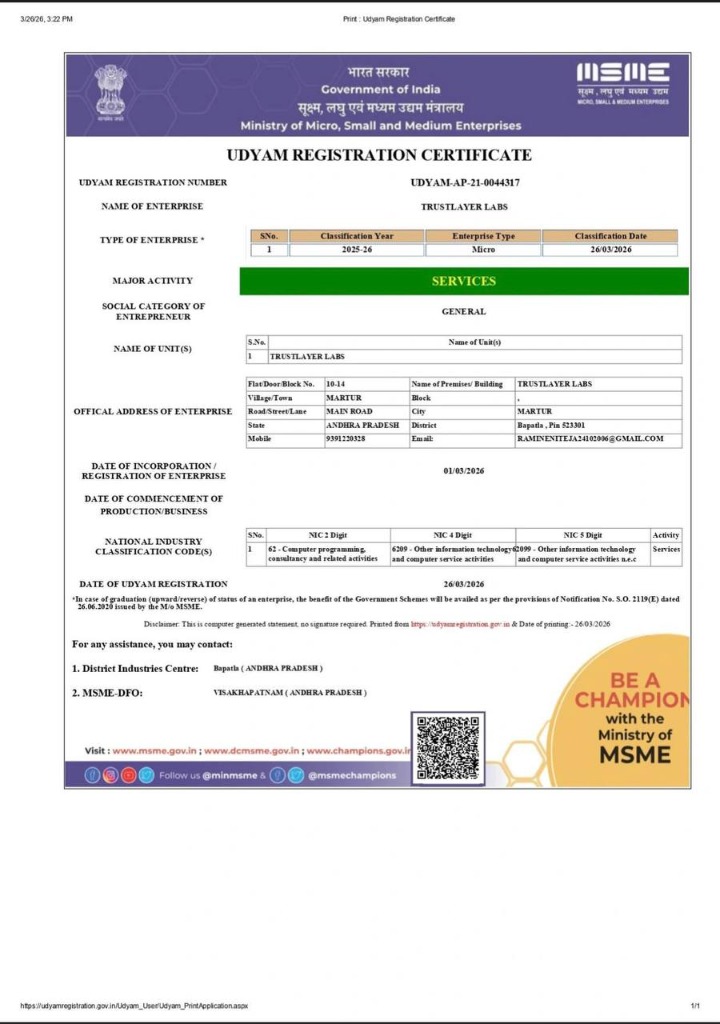
Official Enterprise Registration: TRUSTLAYER LABS
TrustLayerLabs is officially registered as a Micro Enterprise with the Ministry of Micro, Small and Medium Enterprises (MSME), Government of India.
Credibility & Transparency Commitments
“As an emerging offensive security consultancy, TrustLayerLabs rejects manufactured social proof, fake client logos, and inflated experience claims. We earn engineering trust through transparent manual methodologies, reproducible PoCs, mutual NDAs, and verifiable legal accountability.”
Our Core Transparency Guarantees
Zero Fabricated Social Proof & Testimonials
Inquiry: “How does a prospective client verify TrustLayerLabs without past client testimonials?”
Commitment: We do not publish fabricated client reviews or purchased ratings. Instead, we provide our full sample VAPT report and reproducible attack logic so technical leaders can judge our rigor directly.
Illustrative Vulnerability Research & Attack Scenarios
Inquiry: “Are public vulnerability write-ups real client breach engagements?”
Commitment: All published scenarios are research-driven technical breakdowns built on synthetic testbeds and modern frameworks, ensuring zero manufactured customer stories.
Verifiable Practitioner Identity & MSME Entity
Inquiry: “Who executes the security assessments and what legal entity backs the engagement?”
Commitment: Every engagement is led by our founding security architects (IIT Guwahati & VIT Bhopal) holding verified CEH, C3SA, and ISO/IEC 27001 Lead Auditor credentials, backed by our official Govt. of India Udyam MSME registration (UDYAM-AP-21-0044317).